BRIEF
Automate Threat Analysis and Accelerate Response with Splunk and C1
See how Splunk Attack Analyzer automates complex phishing and malware investigations, giving SOC teams consistent threat context while reducing manual effort and response time.
Get your solution brief today!
WHAT TO EXPECT
Automated phishing and malware analysis
Detailed attack-chain visualization
Safe investigation of malicious content
Integrated analysis and response workflows
Faster, more consistent threat decisions
Reduce the Burden on Analysts
Security analysts often spend valuable time moving between disconnected tools, manually examining suspicious content and piecing together attack details. These cumbersome workflows can delay decisions, increase alert fatigue and slow response.
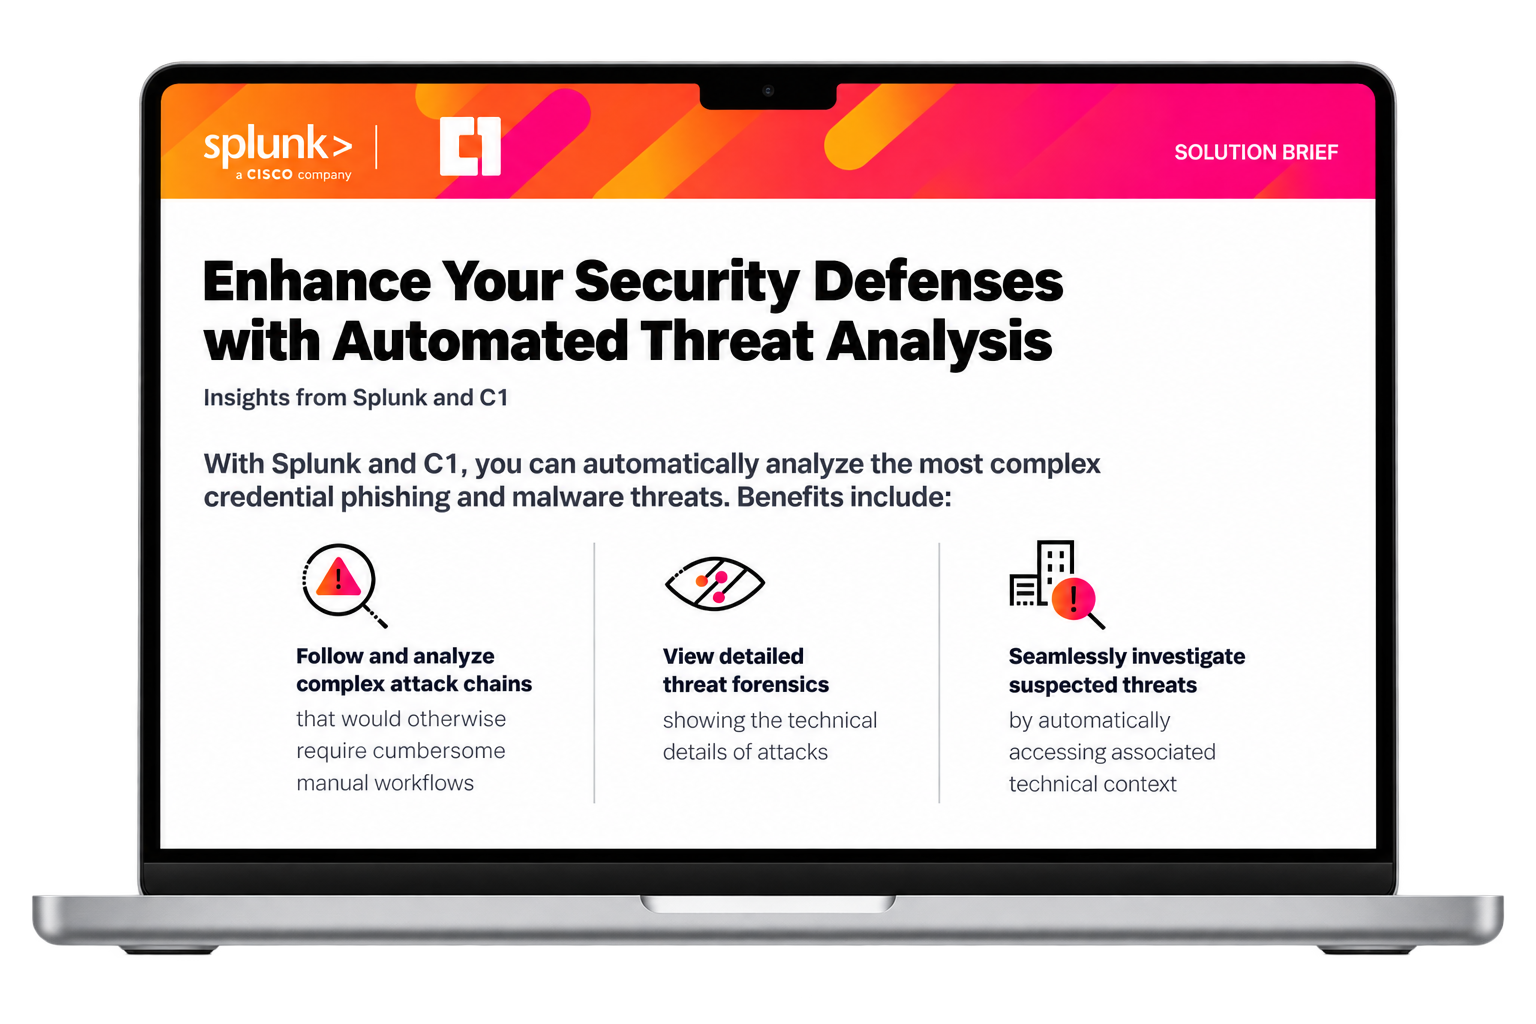
Download the solution brief to see how Splunk Attack Analyzer automates complex phishing and malware analysis, visualizes attack chains and integrates with response workflows—helping SOC teams investigate safely, reach consistent conclusions and respond faster.